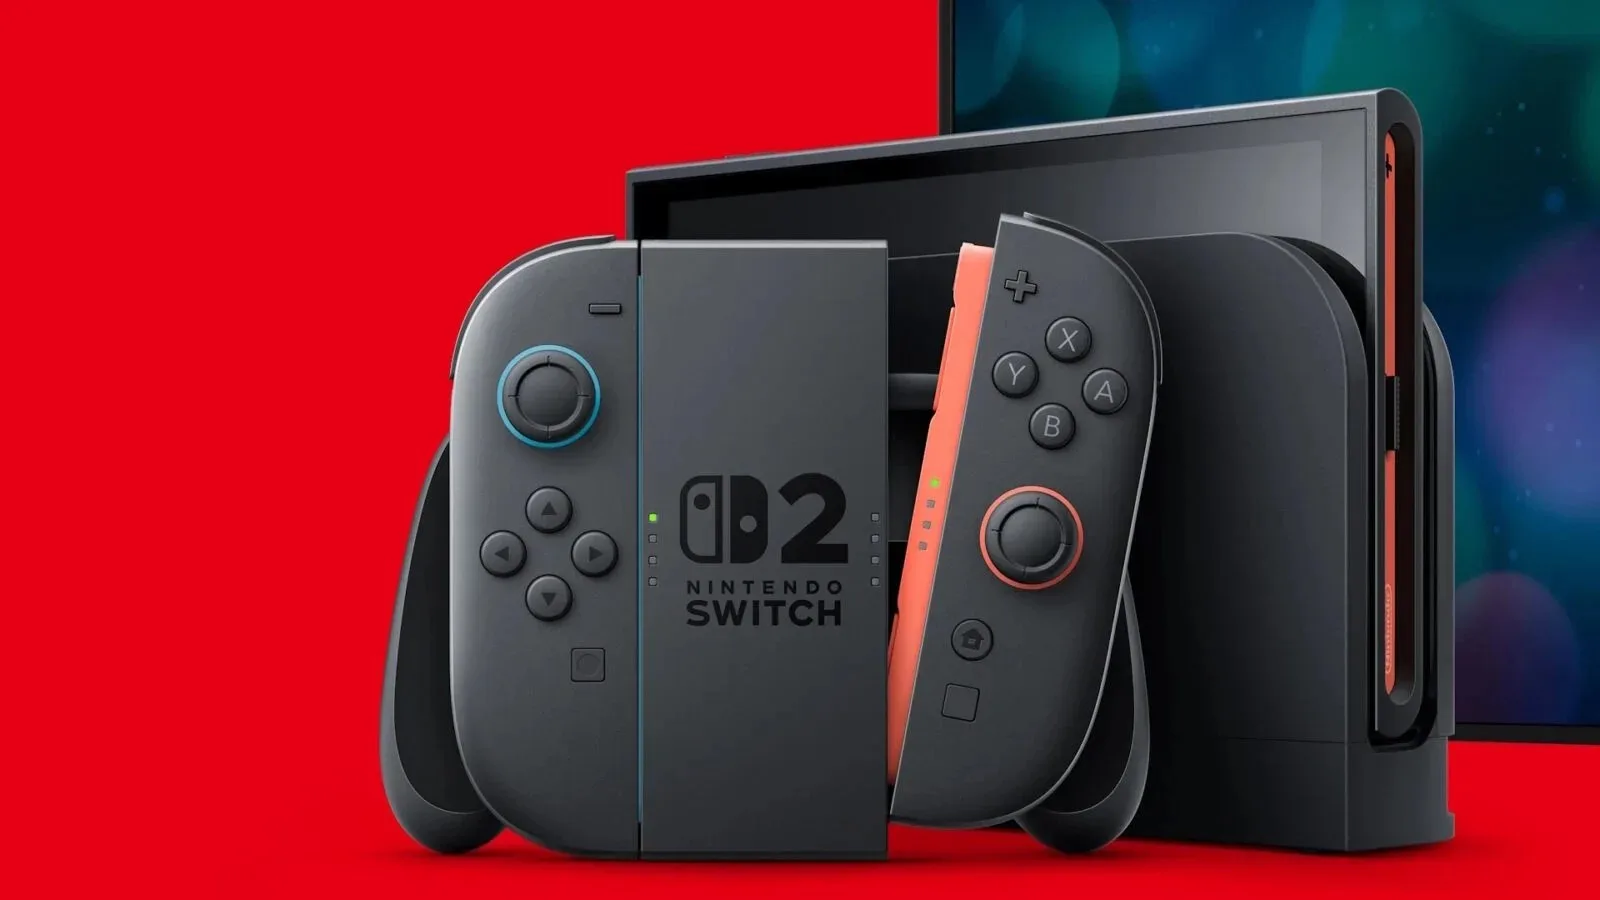
Thanks to the efforts of a few hackers and the support of generative AI models, the first jailbreak for the Nintendo Switch 2 was recently found. Utilizing a copy of the now-delisted Switch app SmileBASIC, a limited exploit allowed users to mod games, install homebrew with the potential to then pirate new games, and download and back up save files. Still, this discovery was limited in the extent to which it could be used to compromise the console’s security. Now, however, hackers have broken beyond these limits using new exploits to further compromise the system security.

These new exploits not only allow modding to occur beyond the limitations of the SmileBASIC software where jailbreaking was first discovered, but have allowed hackers to fully dump and back up the system’s firmware to PC. This new exploit involves hackers gaining access to the Nintendo Switch 2 file system. According to hexkyz as shared by x65943 on the GBAtemp forums, this is done by accessing the file system and overloading the console’s file system and memory. While hackers had previously known how to access the Nintendo Switch file system, it appeared impossible to find a useful exploit for this discovery. However, by using large language models from AI, they were able to find a specific set of actions that could allow the console to read aspects of memory that granted the hackers access to the operations that power the console.
This discovery allows hackers to access “any below-KIP-level binary,” essentially allowing games and apps to be directly dumped to a PC for further modding, as well as the extraction of in-game files. Additionally, now that the exploit and the steps necessary to activate it have been discovered, hackers may be able to find a way to trigger this exploit using applications other than the previously exploited and now-delisted SmileBASIC application. Some hackers are also beginning to investigate whether it may be possible to activate these steps without a specific game or application being required—under the current methods, hacks can only be performed inside other applications and will have to be reactivated after the console has been shut down.
But what does hacking the Switch 2 in this manner actually achieve? For one, it allows for full game dumps and a further examination of how the console functions, opening the door to emulation, piracy and reverse-engineering of Nintendo Switch 2 games.
Though the original Nintendo Switch was also exploited early in its lifespan, allowing for a broad emulation scene to flourish throughout the console’s life, it appeared that the company had managed to prevent a repeat of this vulnerability with their new system. While it’s now almost certain that Nintendo will promptly patch Nintendo Switch 2 to fix these vulnerabilities, this powerful exploit is the first step toward breaking beyond the company’s security measures. With AI systems now aiding such hacking efforts, and the CEOs of AI companies warning that it may soon become impossible to protect software from hacking, the question is whether Nintendo can keep these hackers at bay, or whether a full exploit of Nintendo Switch 2 security is only a matter of time.
Have thoughts, questions, or benchmarks on this topic? Join the discussion on our forums.
Join Discussion ➔



Deltag i samtalen